


Dec 21, 2023 Step by Step Guide to Prepare for MD-101 Exam BrainDumps
Microsoft Windows 10 Release 1809 and later MD-101 Real Exam Questions and Answers FREE Updated on 2023
The MD-101 exam covers a broad range of topics, including device deployment and management, configuration and management of Windows 10 devices and applications, management of updates and policies, implementation of device security solutions, and troubleshooting of desktop and device issues. MD-101 exam is intended for IT professionals who have experience with Windows 10 and Microsoft 365 technologies and who are looking to enhance their skills and credentials in modern desktop management.
Microsoft MD-101 (Managing Modern Desktops) Certification Exam is an advanced level certification exam designed for modern desktop administrators. It is a comprehensive exam that tests the candidate's knowledge and skills in managing and deploying modern desktops, devices, and applications in a Windows 10 environment. Managing Modern Desktops certification exam is designed to validate the candidate's ability to manage and maintain Windows 10 operating systems and associated devices in an enterprise environment.
Microsoft MD-101 exam is a certification exam that validates the knowledge and skills of IT professionals who manage, deploy, and maintain Windows 10 desktops and devices in an enterprise environment. MD-101 exam is a part of the Microsoft 365 Certified: Modern Desktop Administrator Associate certification and covers a wide range of topics related to modern desktop management technologies. Managing Modern Desktops certification is highly respected by employers and is recognized globally, making it a valuable credential for IT professionals who want to enhance their career prospects and increase their earning potential.
NEW QUESTION # 47
Your network contains an on-premises Active Directory domain named contoso.com that syncs to Azure Active Directory (Azure AD).
You have the Windows 10 devices shown in the following table.
You need to ensure that you can use co-management to manage all the Windows 10 devices.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Install the Endpoint Configuration Manager agent on Device1 and Device3.
- B. Join Device 1, Device2, and Device4 to Azure AD.
- C. Enroll Device4 and Device5 in Intune.
- D. Unjoin Device3, Device5, and Device6 from Azure AD, and then register the devices in Azure AD.
- E. Join Device2, Device3, and Device5 to the domain.
Answer: A,C
Explanation:
Co-management enables you to concurrently manage Windows 10 devices by using both Configuration Manager and Microsoft Intune.
Co-management requires Configuration Manager version 1710 or later and enrollment in Microsoft Intune.
Windows 10 devices must be hybrid Azure AD joined.
Reference:
https://docs.microsoft.com/en-us/mem/configmgr/comanage/overview
NEW QUESTION # 48
You use Microsoft Intune to manage Windows updates.
You have computers that run Windows 10. The computers are in a workgroup and are enrolled in Intune. The computers are configured as shown in the following table.
On each computer, the Select when Quality Updates are received Group Policy setting is configured as shown in the following table.
You have Windows 10 update rings in Intune as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 49
Your network contains an Active Directory domain that is synced to Microsoft Azure Active Directory (Azure AD). All computers are joined to the domain and registered to Azure AD.
The network contains a Microsoft System Center Configuration Manager (Current Batch) deployment that is configured for co-management with Microsoft Intune.
All the computers in the finance department are managed by using Configuration Manager. All the computers in the marketing department are managed by using Intune.
You install new computers for the users in the marketing department by using the Microsoft Deployment Toolkit (MDT).
You purchase an application named App1 that uses an MSI package.
You need to install App1 on the finance department computers and the marketing department computers.
How should you deploy App1 to each department? To answer, drag the appropriate deployment methods to the correct departments. Each deployment method may be used once, more than once, or not at all. You may need to drag the split bat between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/intune/apps-add
https://docs.microsoft.com/en-us/sccm/apps/get-started/create-and-deploy-an-application
NEW QUESTION # 50
Your company uses Microsoft Intune to manage devices. You need to ensure that only Android devices that use Android work profiles can enroll in Intune.
Which two configurations should you perform in the device enrollment restrictions? Each correct answer presents part of the solution.
NOTE: each correct selection is worth one point.
- A. From Select platforms, set Android to
- B. From Configure platforms, set Android Personally Owned to
- C. From Configure platforms, set Android Personally Owned to
- D. From Select platforms, set Android work profile to
Answer: A,D
Explanation:
Explanation
https://docs.microsoft.com/en-us/InTune/enrollment-restrictions-set
NEW QUESTION # 51
Your company has computers that run Windows 10 and are Microsoft Azure Active Directory (Azure AD) joined.
The company purchases an Azure subscription.
You need to collect Windows events from the Windows 10 computers in Azure. The solution must enable you to create alerts based on the collected event.
What should you create in Azure and what should you configure on the computers? To answer, select the appropriate options in the answer area.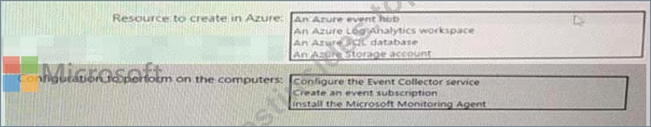
Answer:
Explanation:
NEW QUESTION # 52
You have computers that run Windows 10 and are managed by using Microsoft Intune.
Users store their files in a folder named D:\Folder1.
You need to ensure that only a trusted list of applications is granted write access to D:\Folder1.
What should you configure in the device configuration profile?
- A. Microsoft Defender Application Control
- B. Microsoft Defender SmartScreen
- C. Microsoft Defender Exploit Guard
- D. Microsoft Defender Application Guard
Answer: C
Explanation:
Reference:
https://www.microsoft.com/security/blog/2017/10/23/windows-defender-exploit-guard-reduce-the-attacksurface-
against-next-generation-malware/
NEW QUESTION # 53
Your network contains an Active Directory domain named constoso.com that is synced to Microsoft Azure Active Directory (Azure AD). All computers are enrolled in Microsoft Intune.
The domain contains the computers shown in the following table.
You are evaluating which Intune actions you can use to reset the computers to run Windows 10 Enterprise with the latest update.
Which computers can you reset by using each action? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/intune/device-fresh-start
https://docs.microsoft.com/en-us/intune/devices-wipe
NEW QUESTION # 54
Your company has a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com. All users have computers that run Windows 10. The computers are joined to Azure AD and managed by using Microsoft Intune.
You need to ensure that you can centrally monitor the computers by using Windows Analytics.
What should you create in Intune?
- A. a conditional access policy
- B. a device compliance policy
- C. a device configuration profile
- D. an update policy
Answer: C
Explanation:
Explanation/Reference:
References:
https://www.scconfigmgr.com/2019/03/27/windows-analytics-onboarding-with-intune/
NEW QUESTION # 55
Note: This question is part of a series of questions that present the same scenario. Each question in the
series contains a unique solution that might meet the stated goals. Some question sets might have more
than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these
questions will not appear in the review screen.
Your company uses Windows Update for Business.
The research department has several computers that have specialized hardware and software installed.
You need to prevent the video drivers from being updated automatically by using Windows Update.
Solution: From the Device Installation and Restrictions settings in a Group Policy object (GPO), you enable
Prevent installation of devices using drivers that match these device setup classes, and then you enter the
device GUID.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
References:
https://www.stigviewer.com/stig/microsoft_windows_server_2012_member_server/2013-07-25/finding/WN12-C
NEW QUESTION # 56
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
In the Microsoft 365 Apps admin center, you create a Microsoft Office customization.
Which users can download the Office customization file from the admin center?
- A. Admin1, Admin2, Admin3. and Admin4
- B. Admin1 and Admin3 only
- C. Admin1, Admin2, and Admin3 only
- D. Admin3 only
- E. Admin3 and Admin4 only
Answer: C
Explanation:
* Admin1
An application admin has full access to enterprise applications, applications registrations, and application proxy settings.
* Admin2
Mark your app as publisher verified.
In Azure AD this user must be a member of one of the following roles: Application Admin, Cloud Application Admin, or Global Admin.
* Admin3
Office Apps admin - Assign the Office Apps admin role to users who need to do the following:
- Use the Office cloud policy service to create and manage cloud-based policies for Office
- Create and manage service requests
- Manage the What's New content that users see in their Office apps
- Monitor service health
Reference:
Office Apps admin - Assign the Office Apps admin role to users who need to do the following
https://docs.microsoft.com/en-us/azure/active-directory/develop/mark-app-as-publisher-verified
NEW QUESTION # 57
You have an Azure Active Directory (Azure AD) tenant that contains the named locations shown in the following table.
You need to create a Conditional Access policy that will have a condition to include only trusted locations.
Which two named locations can be marked as trusted? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Location2
- B. Location1
- C. Location4
- D. Location3
- E. Location5
Answer: B,D
Explanation:
Explanation
Location 1 and Location 3, both the ones I had as well as they include the IP Ranges Subnet as Trusted locations
NEW QUESTION # 58
Your network contains an on-premises Active Directory forest named contoso.com that syncs to Azure Active Directory (Azure AD). Azure AD contains the users shown in the following table.
You assign Windows 10 Enterprise E5 licenses to Group1 and User2.
You add computers to the network as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/deployment/windows-10-subscription-activation
NEW QUESTION # 59
Your company has computers that run Windows 10. The employees at the company use the computers.
You plan to monitor the computers by using the Update Compliance solution.
You create the required resources in Azure.
You need to configure the computers to send enhanced Update Compliance data.
Which two Group Policy settings should you configure? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/deployment/update/update-compliance-configuration-manual
NEW QUESTION # 60
You have a Microsoft 365 subscription.
You need to deploy Microsoft Office 365 ProPlus applications to Windows 10 devices.
What should you do first?
- A. From the Device Management admin center, create an app configuration policy.
- B. From Microsoft Azure Active Directory (Azure AD), create an app registration.
- C. From the Device Management admin center, enable Microsoft Store for Business synchronization
- D. From the Device Management admin center, create an app.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/apps-add-office365
NEW QUESTION # 61
Your company has 1,000 Windows 10 devices that are enrolled in Windows Analytics.
You need to view the following information:
The number of devices that are vulnerable to Spectre and Meltdown vulnerabilities The number of devices that have Windows Defender real-time protection turned off Which Windows Analytics solutions should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Note: Windows Analytics is now known as Desktop Analytics and Windows Defender is now known as Microsoft Defender Antivirus
NEW QUESTION # 62
You need to meet the technical requirements for the iOS devices.
Which object should you create in Intune?
- A. An app protection policy
- B. A compliance policy
- C. A Deployment profile
- D. A device profile
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/intune/device-restrictions-configure
https://docs.microsoft.com/en-us/intune/device-restrictions-ios
Topic 2, Litware inc
Existing Environment
Current Business Model
The Los Angeles office has 500 developers. The developers work flexible hours ranging from 11:00 to 22:00. Litware has a Microsoft System Center 2012 R2 Configuration Manager deployment. During discovery, the company discovers a process where users are emailing bank account information of its customers to internal and external recipients.
Current Environment
The network contains an Active Directory domain that is synced to Microsoft Azure Active Directory (Azure AD). The functional level of the forest and the domain is Windows Server 2012 R2. All domain controllers run Windows Server 2012 R2.
Litware has the computers shown in the following table.
The development department uses projects in Azure DevOps to build applications.
Most of the employees in the sales department are contractors. Each contractor is assigned a computer that runs Windows 10. At the end of each contract, the computer is assigned to different contractor. Currently, the computers are re-provisioned manually by the IT department.
Problem Statements
Litware identifies the following issues on the network:
Employees in the Los Angeles office report slow Internet performance when updates are downloading. The employees also report that the updates frequently consume considerable resources when they are installed. The Update settings are configured as shown in the Updates exhibit. (Click the Updates button.) Management suspects that the source code for the proprietary applications in Azure DevOps in being shared externally.
Re-provisioning the sales department computers is too time consuming.
Requirements
Business Goals
Litware plans to transition to co-management for all the company-owned Windows 10 computers. Whenever possible, Litware wants to minimize hardware and software costs.
Device Management Requirements
Litware identifies the following device management requirements:
Prevent the sales department employees from forwarding email that contains bank account information.
Ensure that Microsoft Edge Favorites are accessible from all computers to which the developers sign in.
Prevent employees in the research department from copying patented information from trusted applications to untrusted applications.
Technical Requirements
Litware identifies the following technical requirements for the planned deployment:
Re-provision the sales department computers by using Windows AutoPilot.
Ensure that the projects in Azure DevOps can be accessed from the corporate network only.
Ensure that users can sign in to the Azure AD-joined computers by using a PIN. The PIN must expire every 30 days.
Ensure that the company name and logo appears during the Out of Box Experience (OOBE) when using Windows AutoPilot.
Exhibits
NEW QUESTION # 63
You need to meet the technical requirements for the LEG department computers.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/deployment/update/windows-analytics-azure-portal
NEW QUESTION # 64
You have a Microsoft 365 subscription.
All computers are enrolled in Microsoft Intune.
You have business requirements for securing your Windows 10 environment as shown in the following table.
What should you implement to meet each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://github.com/MicrosoftDocs/IntuneDocs/blob/master/intune/advanced-threat-protection.md
NEW QUESTION # 65
You manage 1,000 computers that run Windows 10. All the computers are enrolled in Microsoft Intune. You manage the servicing channel settings of the computers by using Intune.
You need to review the servicing status of a computer.
What should you do?
- A. From Device configuration - Profiles, view the device status.
- B. From Device compliance, view the device compliance.
- C. From Software updates, view the Per update ring deployment state.
- D. From Software updates, view the audit logs.
Answer: C
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/intune/windows-update-compliance-reports
NEW QUESTION # 66
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains a user named User1. User1 has the devices shown in the following table.
On September 5, 2019, you create and enforce a terms of use (ToU) in contoso.com. The ToU has the following settings:
* Name: Terms1
* Display name: Terms name
* Require users to expand the terms of use: Off
* Require users to consent on every device: On
* Expire consents: On
* Expire starting on: October 10, 2019
* Frequency Monthly
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/terms-of-use#frequently-asked-questions
NEW QUESTION # 67
Your company has a computer named Computer1 that runs Windows 10.
Computer1 was used by a user who left the company.
You plan to repurpose Computer1 and assign the computer to a new user. You need to redeploy Computer1 by using Windows AutoPilot.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/intune/enrollment-autopilot
https://docs.microsoft.com/en-us/windows/deployment/windows-autopilot/windows-autopilot-reset
NEW QUESTION # 68
Your company uses Microsoft Intune to manage Windows 10, Android, and iOS devices.
Several users purchase new iPads and Android devices.
You need to tell the users how to enroll their device in Intune.
What should you instruct the users to use for each device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
The Intune Company Portal app is used to enroll Android, iOS, macOS, and Windows devices References:
https://docs.microsoft.com/en-us/intune-user-help/enroll-device-android-company-portal
https://docs.microsoft.com/en-us/intune-user-help/enroll-your-device-in-intune-ios
https://docs.microsoft.com/en-us/intune-user-help/enroll-your-device-in-intune-macos-cp
NEW QUESTION # 69
Your company has a System Center Configuration Manager deployment that uses hybrid mobile device
management (MDM). All Windows 10 devices are Active Directory domain-joined.
You plan to migrate from hybrid MDM to Microsoft Intune standalone.
You successfully run the Intune Data Importer tool.
You need to complete the migration.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create a new Intune tenant.
- B. Change the tenant MDM authority to Intune.
- C. In Intune, add a device enrollment manager (DEM).
- D. Assign all users Intune licenses.
Answer: B,D
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/sccm/mdm/deploy-use/migrate-hybridmdm-to-intunesa
https://docs.microsoft.com/en-us/sccm/mdm/deploy-use/migrate-prepare-intune
https://docs.microsoft.com/en-us/sccm/mdm/deploy-use/change-mdm-authority
NEW QUESTION # 70
You use Windows Defender Advanced Threat Protection (Windows Defender ATP) to protect computers that run Windows 10.
You need to assess the differences between the configuration of Windows Defender ATP and the Microsoft recommended configuration baseline.
Which tool should you use?
- A. Microsoft Secure Score
- B. Windows Defender Security Center
- C. Windows Analytics
- D. Windows Defender ATP Power BI app
Answer: A
Explanation:
References:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/overview-securescore
NEW QUESTION # 71
You have a Microsoft 365 subscription.
All computers are enrolled in Microsoft Intune.
You have business requirements for securing your Windows 10 environment as shown in the following table.
What should you implement to meet each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://github.com/MicrosoftDocs/IntuneDocs/blob/master/intune/advanced-threat-protection.md
NEW QUESTION # 72
......
Ultimate Guide to Prepare MD-101 Certification Exam for Microsoft Windows 10 Release 1809 and later: https://actualtests.testinsides.top/MD-101-dumps-review.html