


The greatest convenience
I wonder if you noticed that there are three versions of our JN0-232 test questions—PDF, software on pc, and app online, which can bring you the greatest convenience. Imagine that if you feel tired or simply do not like to use electronic products to learn, the PDF version of JN0-232 test torrent is best for you. Just like reading, you can print it, annotate it, make your own notes, and read it at any time. JN0-232 latest torrents simulate the real exam environment and does not limit the number of computer installations, which can help you better understand the details of the exam. The online version of JN0-232 test questions also support multiple devices and can be used offline permanently after being opened for the first time using the network. On buses or subways, you can use fractional time to test your learning outcomes with JN0-232 test torrent, which will greatly increase your pro forma efficiency.
Excellent service
Our customer service is available all day, and your problems can be solved efficiently at any time. Last but not least, we can guarantee the security of the purchase process of JN0-232 test questions and the absolute confidentiality of customer information. You do not have to worry about these issues, because we know that this is a basic condition for us to establish a good business model. At the same time, if you want to continue learning, JN0-232 test torrent will provide you with the benefits of free updates within one year and a discount of more than one year.
Money back guarantee
There are many businesses in the market who boast about the high quality of their test materials. However, we can pat on the chest confidently to say that the passing rate of students who use our JN0-232 test torrent is between 98% and 99%. If you unfortunately fail to pass the JN0-232 exam, upload your exam certificate and screenshots of the failed scores, and we will immediately give a full refund. Using our JN0-232 test questions will not bring you any loss. In addition, the refund process is very simple and will not bring you any trouble. If you have any questions, you can always contact us online or email us. We will reply as soon as possible.
After continuous improvement for years, JN0-232 test questions have built a complete set of quality service system. First of all, JN0-232 test torrent is compiled by experts and approved by experienced professionals. This allows our data to make you more focused on preparation. At the same time, JN0-232 latest torrents provide a free download trial of the PDF version, so that you can understand our products in advance. And according to your needs, you can make the most correct purchase decision without regretting. If there is an update, our system will be automatically sent to you. Secondly, you don't need to worry about any after-sales issues when purchasing JN0-232 test torrent. JN0-232 test questions have the following features:

Juniper JN0-232 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Security Fundamentals | - Network security concepts
|
| Topic 2: VPN and Secure Connectivity | - IPsec VPN fundamentals
|
| Topic 3: Security Policies and NAT | - Policy configuration
|
| Topic 4: Security Services and Monitoring | - Security services overview
|
| Topic 5: Juniper SRX Platform Basics | - Junos security architecture
|
Juniper Security, Associate (JNCIA-SEC) Sample Questions:
Content filtering supports which two of the following protocols? (Choose two.)
- A. TFTP
- B. HTTP
- C. SMTP
- D. SNMP
Correct Answer: B,C 🗳️
Explanation: Only visible for TestInsides members. You can sign-up / login (it's free).
Referring to the exhibit, the top table shows the source and destination IP addresses and also the source and destination ports of the incoming packet.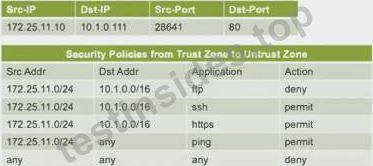
The lower table represents the security policies from the trust zone to the untrust zone.
In this scenario, which two statements are correct? (Choose two.)
- A. The incoming packet is permitted because it does not match any policy listed.
- B. The incoming packet is permitted by the HTTPS application.
- C. The firewall processes security policies in a top-down manner.
- D. The incoming packet is denied by the final security policy.
Correct Answer: C,D 🗳️
Explanation: Only visible for TestInsides members. You can sign-up / login (it's free).
When a new traffic flow enters an SRX Series device, in which order are these processes performed?
- A. routes → zones → screens → security policies
- B. screens → routes → zones → security policies
- C. screens → zones → security policies → routes
- D. screens → security policies → zones → routes
Correct Answer: B 🗳️
Explanation: Only visible for TestInsides members. You can sign-up / login (it's free).
Which two characteristics of destination NAT and static NAT are correct? (Choose two.)
- A. Static NAT uses Port Address Translation.
- B. Destination NAT supports port forwarding.
- C. Static NAT automatically creates a matching rule for the opposite direction.
- D. Destination NAT requires address range sizes that match the devices being translated.
Correct Answer: B,C 🗳️
Explanation: Only visible for TestInsides members. You can sign-up / login (it's free).
Which statement is correct about exception traffic?
- A. Exception traffic is rate-limited on the connection between the Packet Forwarding Engine and the Routing Engine.
- B. Exception traffic is only handled on the Packet Forwarding Engine.
- C. Exception traffic is anything that is rejected by security policies and requires additional processing.
- D. Exception traffic refers to malformed IP packets received on the Packet Forwarding Engine.
Correct Answer: A 🗳️
Explanation: Only visible for TestInsides members. You can sign-up / login (it's free).
Viewing page 1 out of 23 pages.
Viewing questions 1-5 out of 113 questions.


 Upton

 Kelly
 Zara

 Anna
 Gregary

 Alice
 Mortimer
 Letitia
 Christian
 Jane
 Mabel
 Caroline
 Marcus
 Dennis
 Kimberley
 Peter
 Nelly
 Steward
 Renee
 Frank
 Gustave
 Bblythe


